Data privacy (DPDP Act, 2023) · Template

Data breach report to the Data Protection Board of India

Section 8(6) of the DPDP Act requires intimation to the Board and to affected data principals in the event of a personal data breach. The report you file is also the first evidence of how the organisation responded — which is why it should be factual, complete, and written while the timeline is still recoverable.

Quick Statutory Answer

When must a data breach be reported in India? Section 8(6) of the DPDP Act, 2023 requires the data fiduciary to give intimation to the Board and to each affected data principal in the event of a personal data breach, in the form and manner prescribed. Because the prescribed form and timing sit in the rules made under the Act, confirm the current requirement — the safe operating assumption is that it is short.

Draft this document See all 30 templates

Data Breach Report to the Data Protection Board format

The full text of this document as VidhiSar drafts it, with every blank shown in square brackets. Copy it or download it as a Word file and fill it in yourself — or answer a few questions and VidhiSar fills it in and prints a formatted PDF. Clauses that apply only in some cases are left out here; the drafting flow adds them when your answers call for them.

INCIDENT SUMMARY

Date of This Report: [Date of This Report]

Reporting Entity: [Your Business Name] (Registration/Udyam No.: [Business Registration / Udyam Number]) Contact for This Matter: [Contact Email for This Matter]

To, The Data Protection Board of India

Subject: Notification of Personal Data Breach under Section 8(6), Digital Personal Data Protection Act, 2023

DETAILS OF THE BREACH

1. Nature and Discovery. A personal data breach was detected on [Date the Breach Was Detected]. The breach was discovered as follows: [How the Breach Was Discovered].

2. Categories and Volume of Data Affected. The categories of personal data affected are: [Categories of Data Affected]. Based on our initial assessment, approximately [Approx. Number of Individuals Affected] Data Principal(s) are affected by this incident.

3. Root Cause. Our preliminary investigation indicates the following root cause: [Root Cause of the Breach].

4. Containment and Remediation Measures Taken. Immediately upon discovery, we undertook the following containment and remediation measures: [Containment / Remediation Steps Taken]. The current containment status of this incident is: [Current Containment Status].

5. Risk Assessment to Data Principals. We have assessed the potential risk of harm to affected Data Principals arising from this breach and are taking appropriate steps to mitigate such risk, including notifying affected individuals where required.

6. Notification to Affected Individuals. Affected Data Principals are being separately notified of this incident, the categories of data involved, and the protective measures they are advised to take.

UNDERTAKING

We confirm our full cooperation with the Data Protection Board of India in connection with this matter and undertake to provide any further information reasonably requested. This report is submitted in good faith and in a timely manner consistent with our obligations under the DPDP Act, 2023.

Yours faithfully, For [Your Business Name]

Authorised Signatory
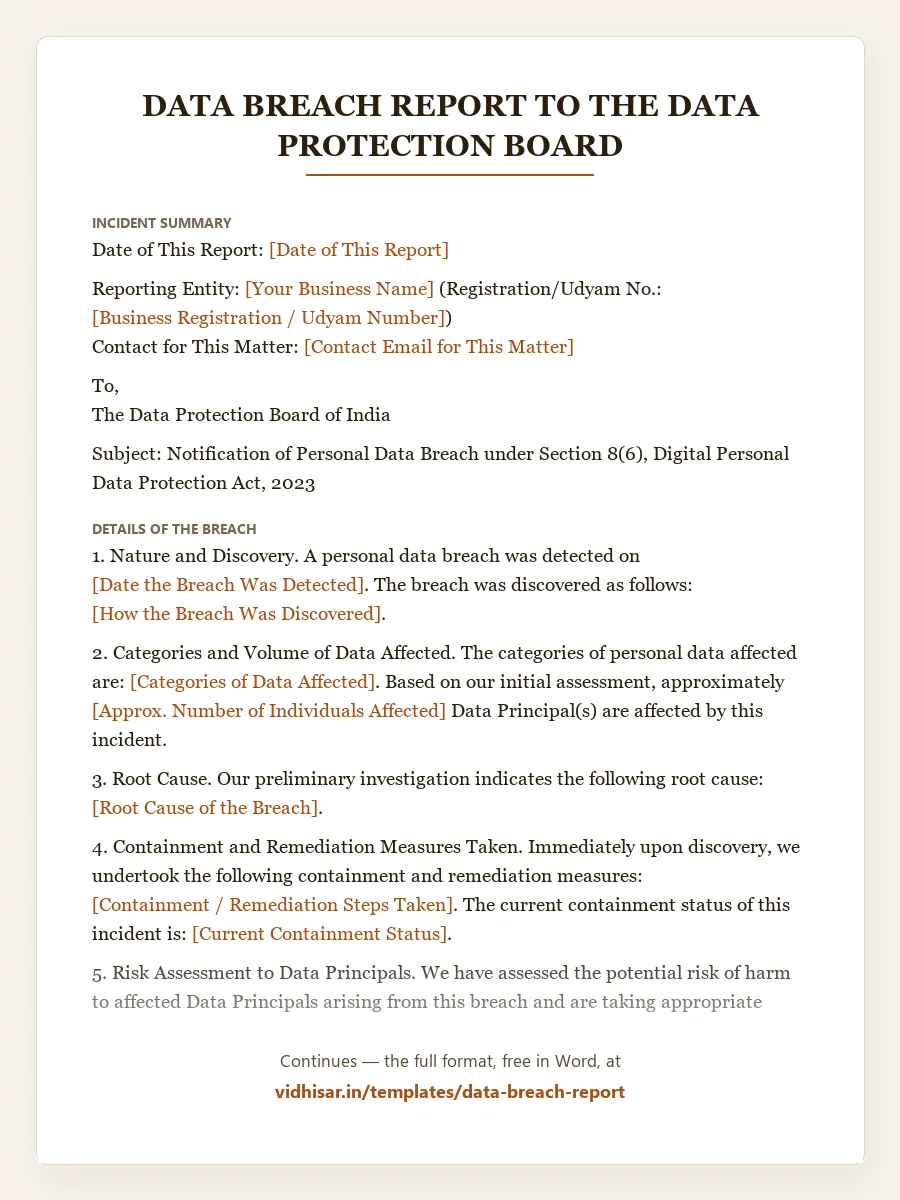
Data Breach Report to the Data Protection Board format (India): page one of the document, with each blank to fill in shown in brackets

Further reading

What the law behind this document actually requires.

  • DPDP Act Penalties Explained: The Up to ₹250 Crore Schedule — Section 33 and the Schedule set penalties from ₹10,000 to ₹250 crore. How the Data Protection Board calculates fines and which breaches cost the most.

Related statutory compliance tools & calculators

  • GST Late Fee Calculator 2026 — Calculate CGST/SGST Section 47 late fees and Section 50 interest
  • TDS Late Payment Interest Calculator — Calculate section 398 interest and section 427 late fees (formerly 201(1A) and 234E)

What this document must contain (Clause-by-Clause Matrix)

Data Breach Report to the Data Protection Board — Mandatory Clause Matrix & Statutory Protection (2026)
Essential Clause Legal Purpose & Protection Governing Law / Benchmark
A factual incident description and timeline What happened, when it began, when it was detected, and how. The gap between occurrence and detection is a fact the report should state rather than obscure. DPDP Act, 2023 — s. 8(6)
The categories of personal data affected Specific categories and, where possible, volume and number of data principals. An estimate stated as an estimate is better than silence. DPDP Act, 2023 — s. 8(4) and (5)
Cause and the point of failure Say what actually failed. A report that avoids the cause is not credible and does not help. DPDP Act, 2023 — the Schedule
Remediation already taken Containment, revocation, patching, notification. Chronological, with dates. DPDP Act, 2023 — s. 8(6)
Measures to prevent recurrence What is changing structurally, not merely that the incident was closed. DPDP Act, 2023 — s. 8(4) and (5)
Notification to data principals The duty extends to affected individuals. State what was sent, to whom, when and how. DPDP Act, 2023 — the Schedule
A named contact A person the Board can reach, with authority to answer. DPDP Act, 2023 — s. 8(6)
  • A factual incident description and timeline — What happened, when it began, when it was detected, and how. The gap between occurrence and detection is a fact the report should state rather than obscure.
  • The categories of personal data affected — Specific categories and, where possible, volume and number of data principals. An estimate stated as an estimate is better than silence.
  • Cause and the point of failure — Say what actually failed. A report that avoids the cause is not credible and does not help.
  • Remediation already taken — Containment, revocation, patching, notification. Chronological, with dates.
  • Measures to prevent recurrence — What is changing structurally, not merely that the incident was closed.
  • Notification to data principals — The duty extends to affected individuals. State what was sent, to whom, when and how.
  • A named contact — A person the Board can reach, with authority to answer.

When you need this

  • On becoming aware of any personal data breach, including one caused by a vendor
  • Where the incident is unauthorised access, disclosure, alteration or loss of personal data
  • When a processor notifies you under their DPA — your duty runs from the breach, not their email
  • Alongside notification to affected data principals, which is a separate limb of the same duty
  • Even where remediation is complete, since the duty is not discharged by having fixed it

The law that governs it

  • DPDP Act, 2023 — s. 8(6) — In the event of a personal data breach, the data fiduciary must give intimation to the Board and to each affected data principal, in the form and manner prescribed. Both limbs apply.
  • DPDP Act, 2023 — s. 8(4) and (5) — The fiduciary must implement appropriate technical and organisational measures and reasonable security safeguards, and engage processors only under a valid contract. A breach report is read against those duties.
  • DPDP Act, 2023 — the Schedule — Failure to take reasonable security safeguards, and failure to give the required breach intimation, are separately addressed in the Schedule of penalties.

Common mistakes

  • Waiting for full root-cause certainty before intimating, when the duty is triggered by the breach
  • Reporting to the Board but not notifying affected data principals, which leaves half the duty undischarged
  • Describing the incident in language that minimises it, which is transparent to any reader and damaging
  • Treating a vendor-caused breach as the vendor's report to make
  • No preserved timeline, so the sequence cannot be reconstructed later

Frequently asked questions

When must a data breach be reported in India?

Section 8(6) of the DPDP Act, 2023 requires the data fiduciary to give intimation to the Board and to each affected data principal in the event of a personal data breach, in the form and manner prescribed. Because the prescribed form and timing sit in the rules made under the Act, confirm the current requirement — the safe operating assumption is that it is short.

Do I have to tell affected customers as well as the Board?

Yes. Section 8(6) has two limbs: intimation to the Board, and intimation to each affected data principal. Reporting to the regulator alone does not discharge the duty.

What if the breach happened at my vendor?

The obligation sits with the data fiduciary. A processor's breach is still your breach to report, which is why a DPA should require the vendor to notify you within a window short enough to leave you able to comply.

Should I report if there was no apparent harm?

The duty in s. 8(6) is expressed by reference to a personal data breach rather than to demonstrated harm. Assessing an incident as harmless and staying silent is a judgement the Board may later review — and the failure to intimate is separately addressed in the Schedule.

Maintained by the VidhiSar Legal Team

Maintains the law explainers, calculators, templates and blog posts on vidhisar.in: checks them against the statute text and updates them when the law changes. Errors and changes in the law can be reported to legal@vidhisar.in.