Data privacy (DPDP Act, 2023) · Template

Customer data breach notification template

The second limb of s. 8(6) is the harder one to write. It goes to the people affected, and its purpose is to let them protect themselves — which means it has to be specific, plain and prompt. A notice that reads like a legal disclaimer fails the only test that matters: whether the reader knows what to do next.

Quick Statutory Answer

Do I have to notify every affected customer individually? Section 8(6) of the DPDP Act, 2023 requires intimation to each affected data principal. The prescribed form and manner sit in the rules made under the Act, so confirm the current requirement — but the obligation is framed around the affected individuals rather than a general public announcement.

Draft this document See all 30 templates

Customer Data Breach Notification format

The full text of this document as VidhiSar drafts it, with every blank shown in square brackets. Copy it or download it as a Word file and fill it in yourself — or answer a few questions and VidhiSar fills it in and prints a formatted PDF. Clauses that apply only in some cases are left out here; the drafting flow adds them when your answers call for them.

Date: [Date of This Notice]

Dear Valued Customer,

WHAT HAPPENED

We are writing to inform you of a data security incident affecting [Your Business Name] that we detected on [Date the Breach Was Detected]. We take the protection of your personal data seriously and are providing you with this notice in the interest of transparency.

WHAT INFORMATION WAS INVOLVED

Our investigation determined that the following categories of your personal data may have been affected: [Categories of Customer Data Affected].

WHAT WE ARE DOING

Upon discovering this incident, we immediately took steps to contain it and secure our systems. We are conducting a thorough investigation and have reported this incident to the Data Protection Board of India in accordance with the Digital Personal Data Protection Act, 2023.

WHAT YOU SHOULD DO

As a precaution, we recommend that you: [Protective Steps You Recommend to Customers]. Please remain vigilant against any suspicious communications purporting to be from us or referencing this incident.

CONTACT US

If you have any questions or concerns about this incident, please contact our support team at [Customer Support Contact Email] or our Grievance Officer at [Grievance Officer Email]. We sincerely apologise for any inconvenience this may cause and remain committed to protecting your personal data.

Yours sincerely, [Your Business Name]
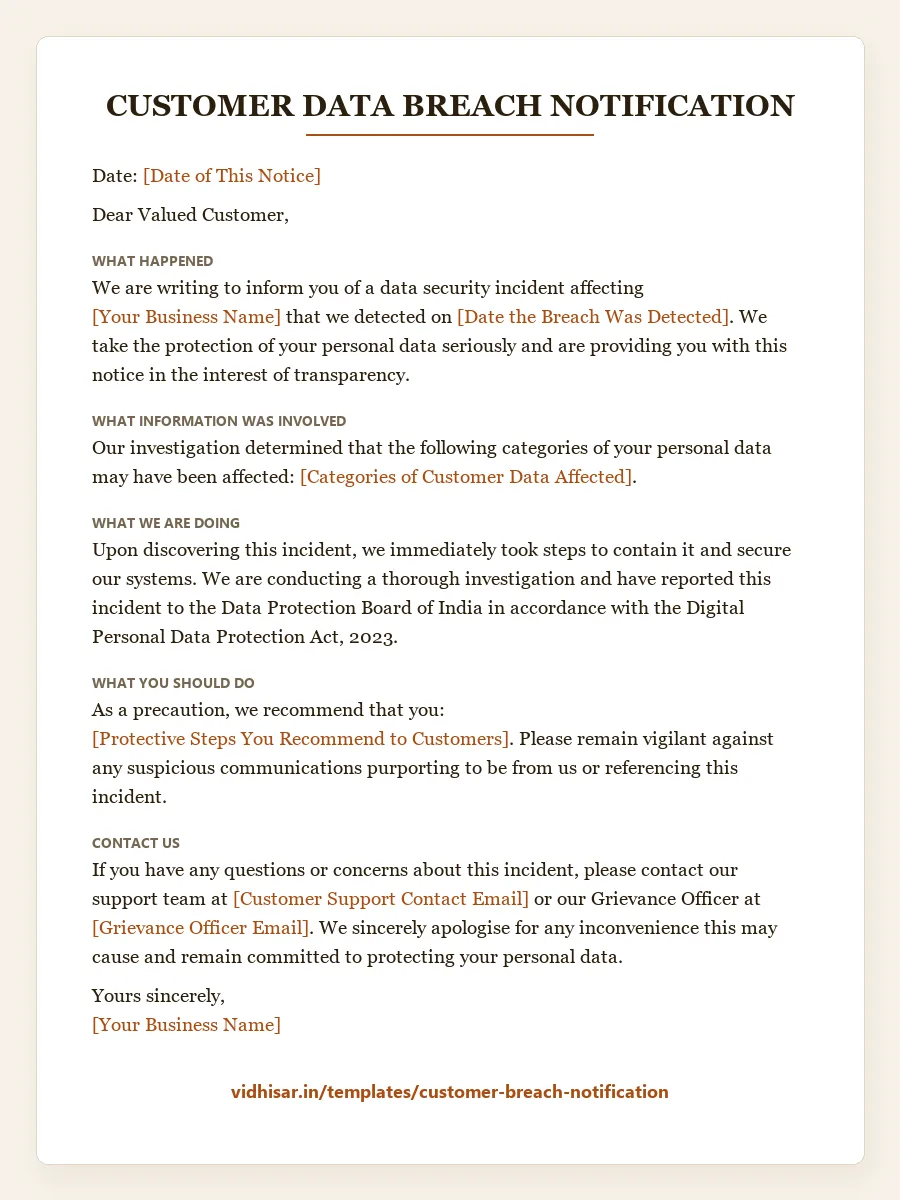
Customer Data Breach Notification format (India): page one of the document, with each blank to fill in shown in brackets

Further reading

What the law behind this document actually requires.

  • DPDP Act Penalties Explained: The Up to ₹250 Crore Schedule — Section 33 and the Schedule set penalties from ₹10,000 to ₹250 crore. How the Data Protection Board calculates fines and which breaches cost the most.

Related statutory compliance tools & calculators

  • GST Late Fee Calculator 2026 — Calculate CGST/SGST Section 47 late fees and Section 50 interest
  • TDS Late Payment Interest Calculator — Calculate section 398 interest and section 427 late fees (formerly 201(1A) and 234E)

What this document must contain (Clause-by-Clause Matrix)

Customer Data Breach Notification — Mandatory Clause Matrix & Statutory Protection (2026)
Essential Clause Legal Purpose & Protection Governing Law / Benchmark
What happened, in plain language Two or three sentences a non-specialist reader understands. Legal phrasing here defeats the purpose of the notice. DPDP Act, 2023 — s. 8(6)
What data of theirs was involved Specific to the recipient where possible. 'Some customer information' tells them nothing they can act on. DPDP Act, 2023 — s. 8(10)
When it happened and when you found out The detection gap will emerge eventually. Stating it is better than being asked about it. DPDP Act, 2023 — ss. 11–13
What you have done Containment and remediation, concretely — so the reader can judge whether the exposure is ongoing. DPDP Act, 2023 — s. 8(6)
What they should do The operative part. Change a password, watch for specific fraud patterns, contact their bank. Be concrete. DPDP Act, 2023 — s. 8(10)
A monitored contact channel A route to a person who can answer follow-up questions, not a no-reply address. DPDP Act, 2023 — ss. 11–13
The grievance route The DPDP framework gives data principals grievance redressal rights. Tell them how to use them. DPDP Act, 2023 — s. 8(6)
  • What happened, in plain language — Two or three sentences a non-specialist reader understands. Legal phrasing here defeats the purpose of the notice.
  • What data of theirs was involved — Specific to the recipient where possible. 'Some customer information' tells them nothing they can act on.
  • When it happened and when you found out — The detection gap will emerge eventually. Stating it is better than being asked about it.
  • What you have done — Containment and remediation, concretely — so the reader can judge whether the exposure is ongoing.
  • What they should do — The operative part. Change a password, watch for specific fraud patterns, contact their bank. Be concrete.
  • A monitored contact channel — A route to a person who can answer follow-up questions, not a no-reply address.
  • The grievance route — The DPDP framework gives data principals grievance redressal rights. Tell them how to use them.

When you need this

  • Alongside the intimation to the Board, as the second limb of the same duty
  • Where a breach exposed customer contact details, identity documents or payment information
  • When credentials may have been exposed and passwords should be changed
  • Where affected individuals may face downstream fraud attempts
  • When a vendor breach touched data belonging to your customers

The law that governs it

  • DPDP Act, 2023 — s. 8(6) — Intimation must be given to each affected data principal as well as to the Board, in the prescribed form and manner.
  • DPDP Act, 2023 — s. 8(10) — The fiduciary must publish the business contact information of a Data Protection Officer or a person able to answer questions about processing. That contact belongs in the notice.
  • DPDP Act, 2023 — ss. 11–13 — Affected individuals retain their rights to information, correction and erasure. A breach notice is a natural moment for those requests, and you should be ready for them.

Common mistakes

  • Writing for the regulator rather than for the customer, so the notice is accurate but useless
  • Omitting what data was involved, which is the one thing the reader needs to assess their own risk
  • No specific protective action, leaving the reader informed and helpless
  • Sending from a no-reply address, which signals the notice is a formality
  • Delaying the customer notice while the internal investigation continues

Frequently asked questions

Do I have to notify every affected customer individually?

Section 8(6) of the DPDP Act, 2023 requires intimation to each affected data principal. The prescribed form and manner sit in the rules made under the Act, so confirm the current requirement — but the obligation is framed around the affected individuals rather than a general public announcement.

What should the notification say?

What happened, what categories of their data were involved, when it occurred and was detected, what you have done, what they should do to protect themselves, and how to reach someone who can answer questions. The test is whether a non-specialist reader finishes it knowing what action to take.

Can I wait until the investigation is complete?

Waiting for full certainty is the most common and most costly error. The duty is triggered by the breach, and a first notice with what is known — updated as more emerges — serves the reader better than a complete notice sent late.

What if only a few customers were affected?

The duty is expressed by reference to affected data principals, not to a volume threshold. A small breach is a smaller notification exercise, not an exemption from one.

Maintained by the VidhiSar Legal Team

Maintains the law explainers, calculators, templates and blog posts on vidhisar.in: checks them against the statute text and updates them when the law changes. Errors and changes in the law can be reported to legal@vidhisar.in.