Data privacy (DPDP Act, 2023) · Template

DPDP-compliant privacy policy template

Most Indian privacy policies are GDPR text with the country name changed. The DPDP Act, 2023 uses its own vocabulary — data fiduciary, data principal, consent manager — and imposes its own duties, and a policy that never mentions them is evidence that nobody read the Act it claims to comply with.

Quick Statutory Answer

Does the DPDP Act apply to my small business? The Act applies to the processing of digital personal data within India, including data collected offline and later digitised, and to processing outside India in connection with offering goods or services to data principals in India. In practice that reaches almost any business with a website, an app, a CRM or a customer database — size is not the test.

Draft this document See all 30 templates

Privacy Policy (DPDP Compliant) format

The full text of this document as VidhiSar drafts it, with every blank shown in square brackets. Copy it or download it as a Word file and fill it in yourself — or answer a few questions and VidhiSar fills it in and prints a formatted PDF. Clauses that apply only in some cases are left out here; the drafting flow adds them when your answers call for them.

PRIVACY POLICY

Effective Date: [Policy Effective Date] Last Updated: [Policy Effective Date]

BUSINESS IDENTITY

[Your Business Name] ("We", "Our", "Company") is a [Business Type] registered in India, operating at [Registered Business Address] and reachable at [Official Contact Email].

1. SCOPE AND APPLICABILITY

This Privacy Policy ("Policy") describes how [Your Business Name] collects, uses, stores, processes, and discloses your personal data in accordance with the Digital Personal Data Protection (DPDP) Act, 2023, the Information Technology (Amendment) Act, 2008, and applicable Rules and Regulations framed thereunder.

2. PERSONAL DATA WE COLLECT

We collect the following categories of personal data: [Types of Personal Data Collected]. This data is collected when you interact with our business through [Collection Channels].

3. PURPOSE OF PROCESSING

Your personal data is processed solely for the following purposes: [Purpose of Data Processing]. We shall not process your data for any other purpose without your prior explicit consent.

4. LEGAL BASIS FOR PROCESSING

We process your personal data on the following lawful bases as recognized under Section 4 of the DPDP Act, 2023: (a) Consent freely given by you prior to collection; (b) Legitimate interests of the business, which do not override your fundamental privacy rights; and (c) Compliance with applicable legal obligations.

5. DATA SHARING AND THIRD PARTIES

We may share your personal data with: [Third Parties Data is Shared With]. All third parties with whom we share data are contractually bound to maintain equivalent data protection standards. We do not sell your personal data.

6. DATA RETENTION

We retain personal data only as long as necessary for the stated purpose or as required under applicable law. Upon expiry of the retention period or upon your valid request, data is permanently deleted or anonymised.

7. YOUR RIGHTS AS A DATA PRINCIPAL

Under Sections 11–14 of the DPDP Act, 2023, you are entitled to: (a) Access a summary of personal data processed; (b) Correct or update inaccurate data; (c) Erasure of your data upon withdrawal of consent; (d) Nominate a representative for data rights; and (e) Lodge a grievance with our Grievance Officer.

8. GRIEVANCE REDRESSAL

For any data privacy concerns, contact our Grievance Officer at: [Grievance Officer / Privacy Contact Email] within 30 days. We shall resolve all grievances within 30 working days. If unresolved, you may escalate to the Data Protection Board of India (DPBI).

9. DATA SECURITY

We implement appropriate technical and organisational measures to protect your personal data against unauthorised access, alteration, disclosure, or destruction, in accordance with IS/ISO/IEC 27001 best practices.

10. AMENDMENTS

We reserve the right to update this Policy. Material changes shall be notified via [How Will Users Be Notified of Changes?] at least 15 days before taking effect.

For queries: [Official Contact Email] | [Registered Business Address]
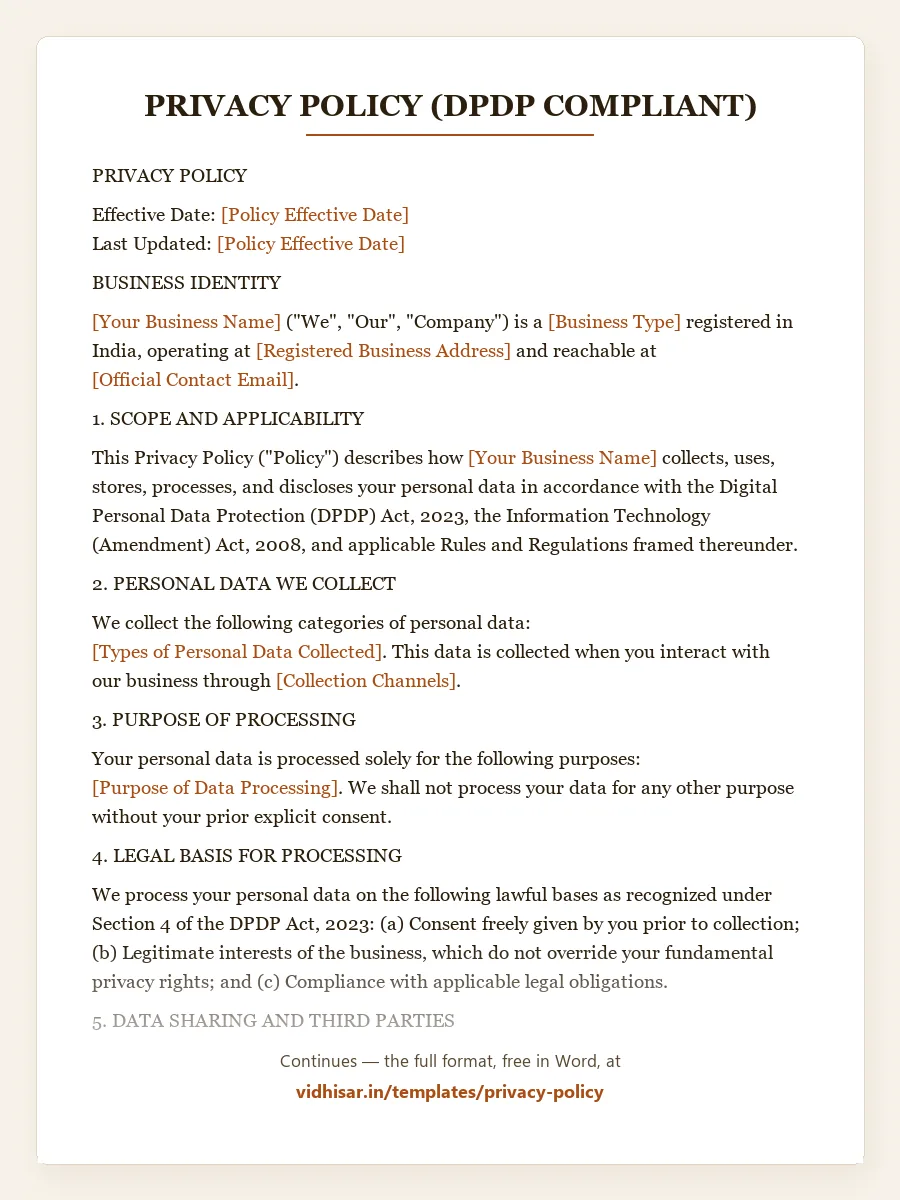
Privacy Policy (DPDP Compliant) format (India): page one of the document, with each blank to fill in shown in brackets

The provision behind this document

  • Section 5, Digital Personal Data Protection Act, 2023 — Before collecting personal data a Data Fiduciary must give a clear notice of what it collects, why, and how consent can be withdrawn. No notice means no lawful collection.
  • Section 6, Digital Personal Data Protection Act, 2023 — Consent must be free, specific, informed and unambiguous. Given for one purpose, it authorises nothing else. Withdrawal must be as easy as giving it.
  • Section 8, Digital Personal Data Protection Act, 2023 — Accuracy, security safeguards, breach reporting, erasure when the purpose ends, and a grievance contact who answers.
  • Section 3, Digital Personal Data Protection Act, 2023 — Digital personal data processed in India, and processing abroad that serves people in India. Paper that is never digitised, personal use, and data the person made public are outside it.
  • Section 9, Digital Personal Data Protection Act, 2023 — Verifiable parental consent before processing a child, and an outright bar on tracking, behavioural monitoring and targeted advertising.

Further reading

What the law behind this document actually requires.

  • DPDP Consent Notice: Checklist and Format for Websites & Apps — Section 5 makes a standalone consent notice mandatory before collecting any personal data. What it must contain, where to place it, and common mistakes.
  • What Is the DPDP Act 2023? Plain-English Summary for Indian Businesses — India’s Digital Personal Data Protection Act explained without legal jargon — who it applies to, the core rules, and what your business must change.
  • DPDP vs GDPR: 7 Key Differences Every Indian Business Must Know — DPDP is not European GDPR with the section numbers changed. Lawful bases, DPO rules, cross-border transfers and penalties compared side-by-side.
  • The DPDP Rules, 2025: the dates your business is actually working to — The Act has been law since 2023 and enforced almost nothing. The Rules notified on 13 November 2025 set the clock — one year for consent managers, eighteen months for everything that touches you.

Related statutory compliance tools & calculators

  • Free DPDP Act 2023 Readiness Check — Assess your business against 21 statutory data protection criteria

What this document must contain (Clause-by-Clause Matrix)

Privacy Policy (DPDP Compliant) — Mandatory Clause Matrix & Statutory Protection (2026)
Essential Clause Legal Purpose & Protection Governing Law / Benchmark
The categories of personal data collected Specific categories, not 'information about you'. A data principal cannot exercise a right over a category they were never told about. DPDP Act, 2023 — the Schedule
The purpose of each processing activity The Act is built around processing for a stated, lawful purpose. Purpose is what a consent notice attaches to, so a policy that lists data without purposes cannot support the consent it relies on. DPDP Act, 2023 — s. 8(5)
How rights are exercised Access, correction, erasure and grievance redressal each need a route the reader can actually use — an address and a realistic response window, not a general contact form. DPDP Act, 2023 — s. 8(6)
A named grievance contact The Act contemplates a readily available means of grievance redressal. An unmonitored inbox is a compliance gap that surfaces at the worst moment. DPDP Act, 2023 — ss. 11–13
Third parties and processors Say who receives the data and why. Each named processor should also sit behind a contract under s. 8(5). DPDP Act, 2023 — the Schedule
Retention and deletion How long data is kept and what triggers deletion. Indefinite retention is a position, and it should be a deliberate one. DPDP Act, 2023 — s. 8(5)
How changes are notified A policy that can change silently offers the reader nothing to rely on. DPDP Act, 2023 — s. 8(6)
  • The categories of personal data collected — Specific categories, not 'information about you'. A data principal cannot exercise a right over a category they were never told about.
  • The purpose of each processing activity — The Act is built around processing for a stated, lawful purpose. Purpose is what a consent notice attaches to, so a policy that lists data without purposes cannot support the consent it relies on.
  • How rights are exercised — Access, correction, erasure and grievance redressal each need a route the reader can actually use — an address and a realistic response window, not a general contact form.
  • A named grievance contact — The Act contemplates a readily available means of grievance redressal. An unmonitored inbox is a compliance gap that surfaces at the worst moment.
  • Third parties and processors — Say who receives the data and why. Each named processor should also sit behind a contract under s. 8(5).
  • Retention and deletion — How long data is kept and what triggers deletion. Indefinite retention is a position, and it should be a deliberate one.
  • How changes are notified — A policy that can change silently offers the reader nothing to rely on.

When you need this

  • If your website, app or POS collects any personal data of individuals in India
  • Before a payment gateway, marketplace or enterprise customer completes vendor onboarding
  • When you begin any marketing that relies on consent you have to be able to demonstrate
  • Where you share data with third parties — delivery partners, analytics, payment processors
  • As the first document to fix after a DPDP readiness assessment, because everything else references it

The law that governs it

  • DPDP Act, 2023 — the Schedule — Penalties are substantial, reaching up to ₹250 crore for certain breaches, and they stack per violation. This is the provision that makes data protection a board-level matter rather than a website chore.
  • DPDP Act, 2023 — s. 8(5) — A data fiduciary may engage a processor to process personal data only under a valid contract. Every vendor named in your policy should have one.
  • DPDP Act, 2023 — s. 8(6) — In the event of a personal data breach, the fiduciary must give intimation to the Board and to each affected data principal in the prescribed form and manner.
  • DPDP Act, 2023 — ss. 11–13 — Data principals have rights to access information about processing, and to correction, completion, updating and erasure. Your policy has to describe how each is exercised.

Common mistakes

  • Publishing GDPR text with 'India' substituted, which uses the wrong terminology and misses the Act's own duties
  • Listing data categories without stating the purpose each is processed for
  • Naming a grievance contact that nobody monitors
  • Claiming a lawful basis the Act does not use, borrowed from another jurisdiction
  • Never revisiting the policy after adding a new processor, so the disclosure and the reality diverge

Frequently asked questions

Does the DPDP Act apply to my small business?

The Act applies to the processing of digital personal data within India, including data collected offline and later digitised, and to processing outside India in connection with offering goods or services to data principals in India. In practice that reaches almost any business with a website, an app, a CRM or a customer database — size is not the test.

Is a GDPR privacy policy enough for India?

No. The DPDP Act uses its own concepts and duties — data fiduciary and data principal rather than controller and subject, its own consent notice requirements, its own breach intimation duty under s. 8(6), and its own rights under ss. 11 to 13. A GDPR policy will be missing those and will describe bases the Indian Act does not use.

What are the penalties under the DPDP Act?

The Schedule to the Act sets out financial penalties for different classes of breach, reaching up to ₹250 crore, and they apply per violation. The amount in any given case is determined by the Data Protection Board having regard to the factors the Act specifies.

Do I need a privacy policy if I only use WhatsApp for orders?

If you collect names, phone numbers, addresses or payment details of individuals in India, you are processing personal data, and the channel does not change that. The obligations attach to the processing rather than to having a website.

Maintained by the VidhiSar Legal Team

Maintains the law explainers, calculators, templates and blog posts on vidhisar.in: checks them against the statute text and updates them when the law changes. Errors and changes in the law can be reported to legal@vidhisar.in.